Cyberattack hits Trump administration as hackers take down USDA
The US Department of Agriculture was affected by a cyberattack this week in the latest takedown of a trusted institution.
NBC News reported the hack on Friday, citing two former USDA officials with knowledge of the matter.
Hackers gained access to the department’s system that facilitates payment to farmers, the agency told employees on Thursday, the sources said.
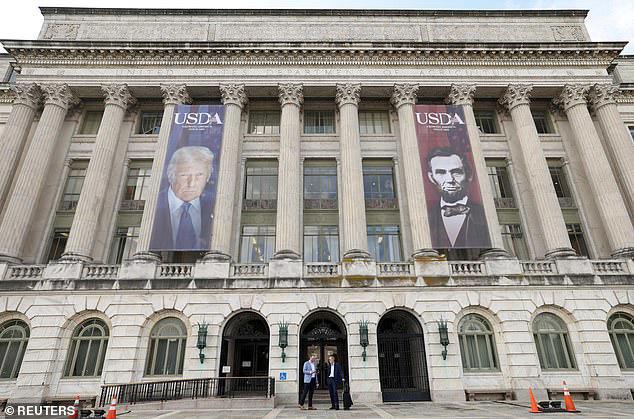
The department notified employees of the incident on Thursday, the former officials told NBC.
While the payments database is the known extent of the intrusion so far, the former officials warned that the compromised system could provide a backdoor to more sensitive information, including food safety data and research on animal-borne illnesses, according to the report.
It is not known who was responsible.
Donald Trump told the media on Friday that each of the outages was ‘separate’ and not a mass attack.
The Daily Mail has reached out to the White House and the Department of Agriculture for comment.
The Cybersecurity and Infrastructure Security Agency referred questions to the USDA, which did not immediately respond to a request for comment.
It comes after a spate of outages and attacks, which began a week ago when Microsoft Outlook spent nearly a full day down.
The following day, the FAA announced a national ground stop for just the second time since 9/11 due to a system error.
Since then, everything from banks to airlines have experienced outages, with customer data potentially having been stolen.
On Thursday, officials for Chase, America’s biggest bank, revealed that ‘customer names and email addresses’ may have been stolen during the cyberattack.
Credit card giants Visa and Mastercard were also impacted by the same breach orchestrated by one ransomware group, which claimed to have the private records, phone numbers and even dinner and hotel reservations of ‘tens of thousands’ of customers.
Cybersecurity firm SOCRadar revealed that the attack was carried out by a group called n0n, which claimed responsibility for the breach on the dark web.
According to both Chase, the everyday consumer banking brand, and JP Morgan, the bank’s investment and corporate wing, the hack targeted third-party vendors with access to the financial giant’s marketing data.
Visa revealed that one of their third-party service providers in the Asia-Pacific region was impacted by the breach, but payment data and credit card numbers were not part of the information stolen.
A Mastercard spokesman said the cyberattack only affected a small number of cardholders who were enrolled in a specific rewards program.
In a public statement, Chase claimed that the cyberattack was not tied to the ongoing global outages affecting banks, tech giants and federal agencies over the last week.
JPMorgan Chase added that there were no additional disruptions to the bank’s services connected with this hack.
Bank officials did not provide details on how many customers may have been affected by the breach and said they would be contacting affected customers to provide support and free credit monitoring protection ‘where appropriate.’
JPMorgan Chase is the largest bank in the US and one of the biggest in the world. The bank holds roughly $5.1 trillion in assets, and it runs the country’s biggest branch network with over 5,000 locations.
The bank serves about 86 to 87 million individual customers and more than seven million small businesses with checking accounts, savings accounts, credit cards and other everyday banking services.
SOCRadar said in a report on the hacking group: ‘n0n is a financially motivated cyber extortion group that emerged in September 2026, focusing on data theft and extortion without relying on traditional ransomware.’
It is believed that the attack on Chase, Visa and Mastercard was carried out on or around November 16, the same day Chase and other major banks were impacted by a massive systems outage.
A spokesperson for Chase told the Daily Mail on November 16 that the outage was caused by a ‘software bug in on-premise hardware systems’ and the bank had no evidence the problems were the result of cyberattacks.
The Daily Mail has reached out to Chase for comment.
Those outages followed catastrophic meltdowns of both Microsoft’s Outlook email system and the Federal Aviation Administration’s communications network for US flights.
Officials in the Trump Administration and some tech insiders have claimed that many of the outages have stemmed from companies and federal agencies now using AI to quickly identify software issues and patch these systems in real-time.
The overwhelming number of system patches, meant to stay ahead of cybercriminals, was allegedly causing problems with the software coding than ran the systems of many companies and government agencies.
However, cybersecurity experts, including Digitalwarfare.com’s James Knight, have maintained that the pattern and sheer number of outages was too suspicious to simply be a string of poor software updates issued by multiple independent companies.
It is unclear at this time if the cyberattack on Chase’s third-party vendors was related to the discovery of malware affecting companies using Optimizely.
The reveal of the USDA hack comes a day after Sean Cairncross was sacked as National Cyber Director.

